AI & Data Protection Consulting
External Data Protection Officers at a flat-rate price
Data Protection Flatrate
DPA, PIA, Records of Processing Activities and more. One flat price.
Data Protection Officer
We appoint the Data Protection Officer for you and take care of the paperwork.
GDPR Audit
GDPR Compliance Audit – Fit-Gap analysis or full audit. We check your compliance status and provide actionable recommendations.
GDPR, AI Act, Data Act
We advise on everything data protection related. Don’t worry!
NIS2, ISO 27001, IT-SiG
Data Security does mean IT- and InfoSec as well.
Business oriented
Our credo: Reports for management. Best Practice for all others.
Reaction times
We answer within 24 hours, no matter which package you choose. In urgent cases right away.
Security
Encryption by default. Data you share with us is hosted on secure German servers.
Supervisory authorities
Profit from our experience with the authorities. We happily support you with any request.
Best Practice Consulting
Legal expertise with a hands-on mentality
Focus usually
Focus with us
Fresh Compliance offers fresh, pragmatic, and legally robust data protection consulting. Responses typically take <24 hours, and often it is much quicker. If it ever takes longer, we will let you know. Our prices are flat-rates and fully transparent. There are no hidden costs, fine print, or unfair contracts. An automated, bi-annual feedback process ensures that we continuously improve, thanks to you
Our goal is customer satisfaction. We get there through transparent pricing in our consulting packages: no hidden fees, no surprises and no more billing by the hour!
We know how important quick responses are. If we can't answer within 24 hours, you still get a timely update. Audits by the authorities and Data Breaches will be prioritized.
Custom-tailored consulting sounds like a phrase? Let's prove otherwise. We do not write generic reports and we do not ask for department structures in an early stage startup, promised!
Physical meetings and constant updates. We love talking to the people in your company. Regular data protection routines and management reviews are included. You become compliant and we can take over more tasks.
References
We are proud of many hundreds of projects. In addition to international startups and systemically important SMEs, we also advise the most significant AI companies in Europe


Data Protection at a Fixed Price
Easy to understand pricing structures with no fine print
Start
monthly
399€
Term: 1 year
 Appointment of the data protection officer
- Data protection consulting (24 hrs per year)
- Compilation of all data protection documents
- Data protection eLearning incl. (up to 50 employees)
- Data security eLearning incl. (up to 50 employees)
- AI basics eLearning incl. (up to 50 employees)
- Privacy badge included
Perfect for startups and small businesses – longer-term consulting with a calculable budget
RequestExtra
monthly
699€
Term: flexible
- Appointment of the data protection officer
- Data protection consulting (normal demand)
- Compilation of all data protection documents
- Data protection eLearning incl. (up to 150 employees)
- Data security eLearning incl. (up to 150 employees)
- AI basics eLearning incl. (up to 150 employees)
- Privacy badge included
Ideal middle ground for those who want to remain flexible in terms of term and costs on a monthly basis
RequestFlatrate
monthly
999€
Term: flexible
- Appointment of the data protection officer
- Data protection consulting (unlimited / fair use)
- Compilation of all data protection documents
- Data protection eLearning incl. (up to 500 employees)
- Data security eLearning incl. (up to 500 employees)
- AI basics eLearning incl. (up to 500 employees)
- Privacy badge included
The all-inclusive package for many data protection issues, flexible rebooking at any time
RequestAudits and workshops
Have two of our consultants review your company or your processes
GDPR Audit
from 4990€
Fixed pricing, depending on company size
- On-site interviews by two consultants (1-2 days)
- Professional data protection audit with the contact persons
- Preparation of a comprehensive, risk-based report
- Easy to implement action plan included
- Perfect for funding rounds, inspections, or certifications
Founder Team
Two founders and a continuously growing team are by your side
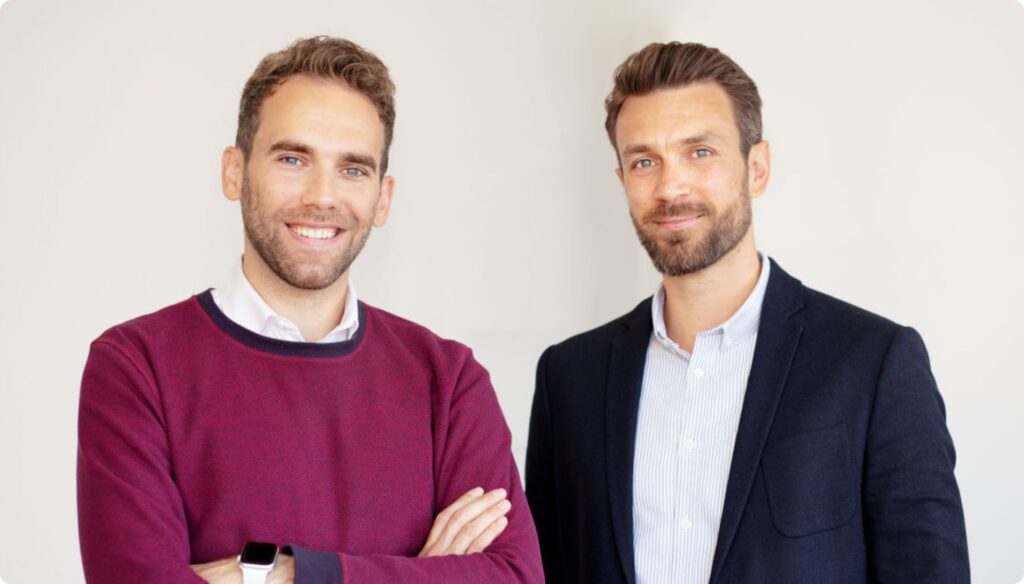
Frank Trautwein
… is specialized in technology law and had been a senior consultant for Data Protection & IT-Security for many years. Besides print and online publications, he gives talks and webinars on practical implementation of the GDPR. As certified Data Protection Officer and Lead Auditor (ISO 27001) he develops Information-Security and Data Protection Managementsystems.
Philipp Heindorff
… works as a lawyer and is specialized in Data Protection and Tech Law. Thanks to his extensive experience he is consulting companies from startup to corporate. He advises companies in the IT sector and digital economy as a certified Data Protection Officer and was involved in different matters of supervisory authorities. His focus is on risk analysis and business-oriented Data Protection Management.
FAQ
Here are some frequently asked questions and their answers about our data protection services
What is GDPR?
GDPR stands for General Data Protection Regulation. It’s an EU law (“regulation”) on data protection and privacy for all individuals in the European Union and the European Economic Area. Its main purpose is to give individuals more control over their personal data and to harmonize the regulatory environment for businesses.
When do we have to appoint a Data Protection Officer?
A Data Protection Officer (DPO) must be appointed if: the processing is carried out by a public authority or body; the core activities of the controller or processor consist of processing operations that require regular and systematic monitoring of data subjects on a large scale; or if the core activities involve processing on a large scale of special categories of data (e.g., health data, racial or ethnic origin, etc.) or data relating to criminal convictions and offenses. In addition to the GDPR requirements, according to the German BDSG, a DPO must also be appointed if a company regularly employs at least 20 people involved in the automated processing of personal data. Furthermore, the appointment of a DPO is mandatory if there are processing operations that require a data protection impact assessment, i.e., those with a high risk to the data subjects.
What does the DPO do?
The Data Protection Officer (DPO) has a control function and supports employees as well as customers with all questions relating to GDPR. They oversee data protection strategy and implementation to ensure compliance. The DPO is your main contact for all data protection related questions.
Who does GDPR apply to?
The GDPR applies to organizations operating within the EU and organizations outside of the EU that offer goods or services to, or monitor the behavior of, EU data subjects. It applies to all companies processing and holding the personal data of data subjects residing in the European Union.
Where does GDPR apply?
GDPR is extraterritorial in its scope. It applies to any organization based within the EU, regardless of whether the data being processed concerns individuals in the EU or non-EU individuals, such as those from the United States or Australia. So, even if our company, based in the EU, processes data of citizens or individuals from non-EU countries, the data processing is still subject to GDPR rules. It emphasizes the global reach of GDPR and the importance of compliance regardless of the nationality or residence of the data subject.
What is considered “personal data” under GDPR?
Personal data is any information that relates to an identified or identifiable individual. Examples include name, email, address, phone number, IP address, and location data. It can be broad and includes any information that can be used directly or indirectly to identify a person. A hashed or encrypted e-mail address uploaded to Facebook Custom Audience might be personal data for them since they can match it with an existing user’s e-mail address.
How does GDPR affect marketing activities?
Under GDPR, organizations must obtain clear and unambiguous consent from individuals before processing their data for marketing purposes or for tracking purposes. This means pre-ticked boxes or inactivity cannot constitute consent. Also, individuals have the right to withdraw their consent at any time.
What are the consequences of not complying with GDPR?
Non-compliance can result in severe penalties, including fines up to €20 million or 4% of the company’s global annual revenue (whichever is higher). Apart from financial penalties, non-compliance can also damage an organization’s reputation. Many well-known data breaches of Tech companies speak for themselves.
How much does an external DPO cost in Germany?
At Fresh Compliance, external Data Protection Officer services start at 399 EUR per month. Compared to hourly providers charging 150-300 EUR per hour, our flat-rate offers full cost transparency.
What is included in your GDPR compliance service?
Our packages include: appointment as your external DPO, complete documentation, employee training, and ongoing consulting – all at one transparent monthly price.
Contact us
Send us an e-mail or give us a call – we usually answer within 24 hours.